NORA Delivers Value to Both Sides
of the Risk Assessment
Most tools serve the security team. NORA is the first platform built to serve both the people doing the assessment and the people receiving the output — simultaneously.
The Asset Owner
The person who knows the system
They understand how the business runs but have never been taught cybersecurity language. NORA guides them through a plain-English conversation, turning their operational knowledge into structured risk data — without requiring a security background.
- Answers questions they can actually answer
- No jargon, no guessing, no handing it back to IT
- Contributes meaningfully to the organization's risk posture
- Completes an assessment in 20–40 minutes
The GRC Professional
The person who needs the output
Whether in-house or consulting, they know the asset owner holds a wealth of knowledge about how their systems really work — the challenge has always been accessing it, because security questions are framed in language the business doesn't speak. NORA does that for them: it asks in plain business language, surfaces what the owner already knows, and hands back structured, translated, defensible output — so the conversation finally captures the treasure that was there all along.
- Receives audit-ready narratives from business conversations
- Scores are defensible, contextualized, and traceable
- Eliminates the back-and-forth interpretation cycle
- Every narrative traceable to the owner's actual answers
When the Stakes Are Highest, NORA Is Ready
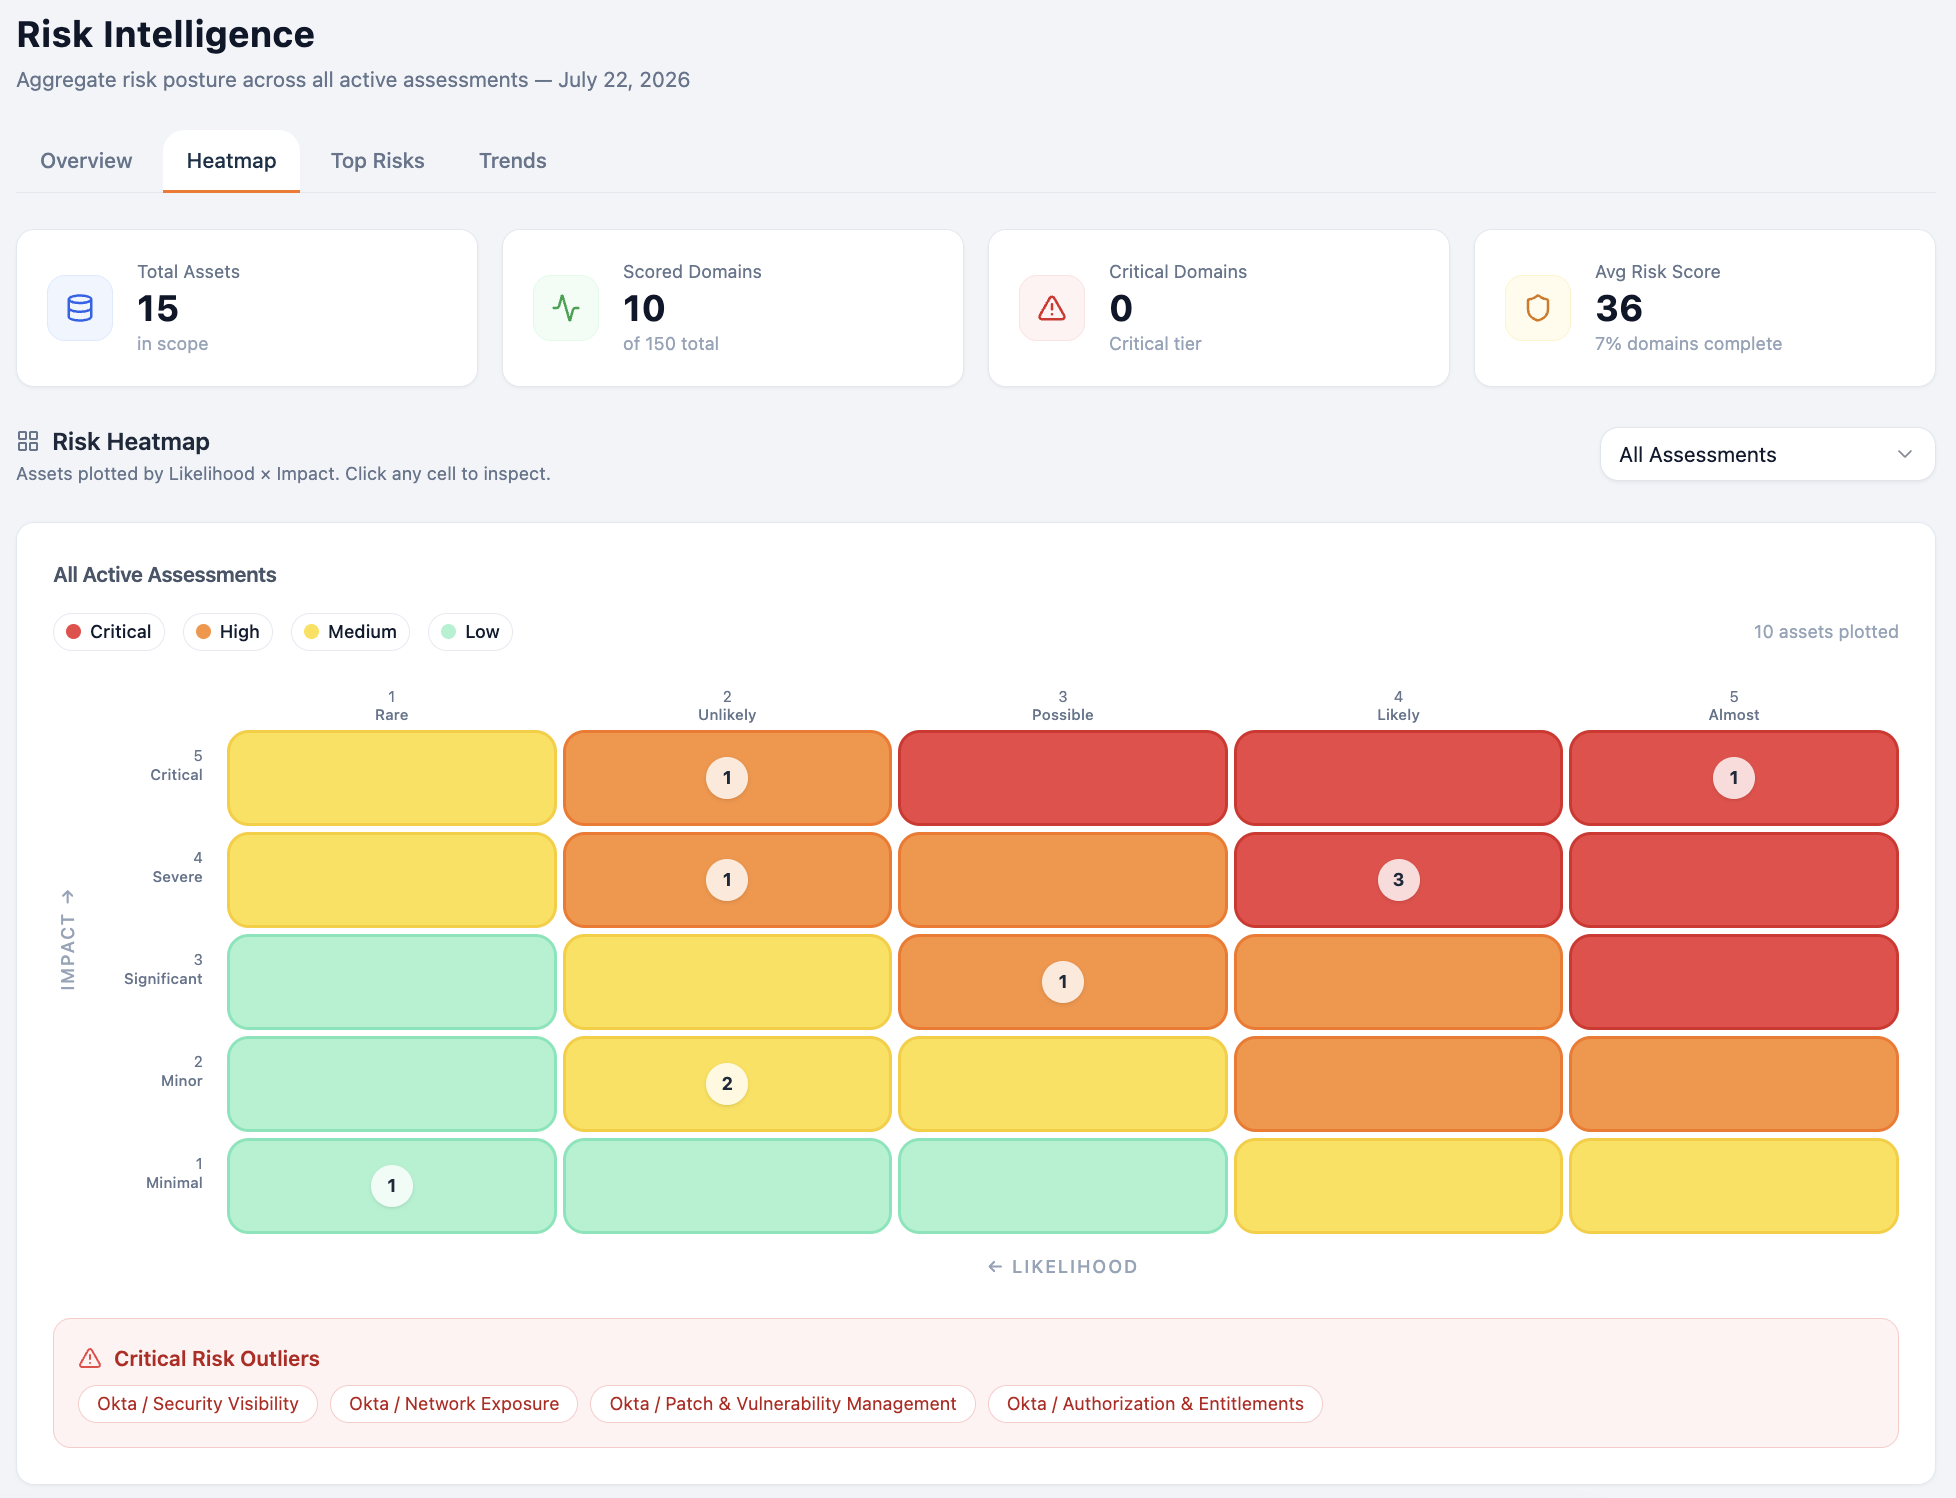
Inaccurate or undocumented risk assessments carry their highest cost exactly when the stakes are highest. NORA structures your assessment to meet each of these moments with output that is accurate, defensible, and ready to use.
SOC 2 Readiness
Map completed risk domains to Trust Services Criteria automatically.
ISO 27001 Gap Assessments
Identify control gaps across ISO domains with context-aware scoring.
Board-Level Risk Reporting
Present a defensible risk posture with scores that reflect business reality.
Cyber Insurance Applications
Document controls and risk posture with structured, traceable evidence.
M&A Due Diligence
Rapidly assess acquisition targets using the same methodology as your own systems.
Risk Posture Visibility
Go beyond compliance documentation. A clear, ongoing picture of where risk actually lives.
A Structural Advantage Competitors Can't Copy Quickly
The problem NORA solves is widely acknowledged and poorly solved by existing tools. What makes NORA different is the depth of practitioner knowledge embedded in the product.
01
Practitioner Knowledge Embedded in the Architecture
The questions NORA asks, the way they are framed for an asset owner, the domains they cover, and the translation output all reflect how risk assessments actually work in practice — not how they are described in documentation. That depth is baked into the product in ways that take years to accumulate and cannot be replicated by a software team working from the outside.
02
An Inverted Model Nobody Else Has Built
Every GRC platform on the market is built from the auditor perspective downward — expecting asset owners to learn the language of controls frameworks. NORA inverts that model. It speaks the asset owner's language, then translates upward into the auditor's language. The people with the most relevant operational knowledge are no longer excluded from the assessment process.
03
Designed for How Most Organizations Actually Operate
Hundreds of thousands of organizations are conducting formal risk assessments for the first time — driven by new regulatory requirements, insurance mandates, and board-level pressure. Most have no dedicated GRC team. Every existing tool assumes one exists. NORA is built specifically for organizations doing this without a specialist in the room.